In our increasingly digital world, data has become one of the most valuable assets for businesses and individuals alike. However, this value comes with an array of risks, including cyberattacks, insider risks, and accidental leaks, and the need for effective measures to prevent data loss is more critical than ever.
What is Data Loss Prevention?
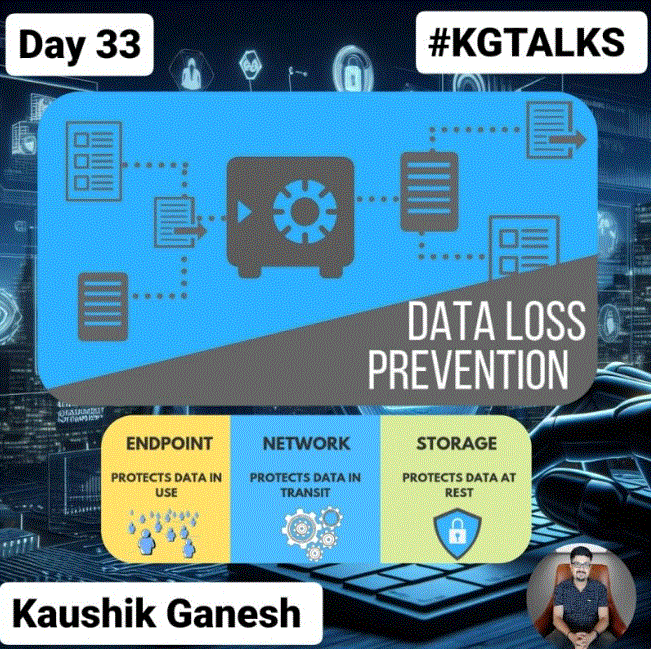
DLP is a set of tools and processes used to ensure that sensitive or critical information is not lost, misused, or accessed by unauthorized users. It involves identifying, monitoring, and protecting data in use (endpoint actions), data in motion (network traffic), and data at rest (data storage).
Why is DLP Important?
1. Protecting Sensitive Information: DLP helps protect sensitive information such as personal identifiable information (PII), intellectual property, financial data, and more from getting into the wrong hands.
2. Regulatory Compliance: Many industries have regulations requiring them to protect certain types of data. DLP can help organizations comply with these regulations and avoid hefty fines.
3. Preventing Insider Threats: Not all data breaches come from outside an organization. Sometimes, they can be the result of actions taken by employees, whether intentional or accidental. DLP can help prevent such insider threats.
Why Prioritize DLP?
1. Improve Data Visibility: DLP solutions provide better visibility into data management, storage, access, and usage.
2. Secure Remote and BYOD Environments: DLP software enforces security policies for remote and Bring Your Own Device (BYOD) workers, maintaining consistency across teams and locations.
3. Protect Intellectual Property: A robust DLP strategy shields critical assets.
4. Maintain Brand Reputation: Data breaches erode customer trust.
5. Prevent Cyberattacks: DLP helps prevent breaches and their associated costs.
Implementing a DLP Strategy!
1. Assess Your Data: Identify sensitive data across your organization—where it resides, who accesses it, and how it’s used.
2. Define Policies: Create clear guidelines for data handling, access controls, and encryption.
3. Choose DLP Software: Select a robust DLP solution that aligns with your organization’s needs.
4. Educate Employees: Train staff on data security best practices.
5. Monitor and Adapt: Continuously monitor data flows, adjust policies, and stay informed about emerging threats.
Remember, Remember, DLP is not just about technology; it’s also about people and processes. By prioritizing data protection, you’re not only safeguarding the organization but also building trust with their customers and partners.
I hope you find this post useful and informative. Please feel free to share your thoughts and feedback in the comments. Stay tuned for more posts on cybersecurity, risk and compliance in the coming days.