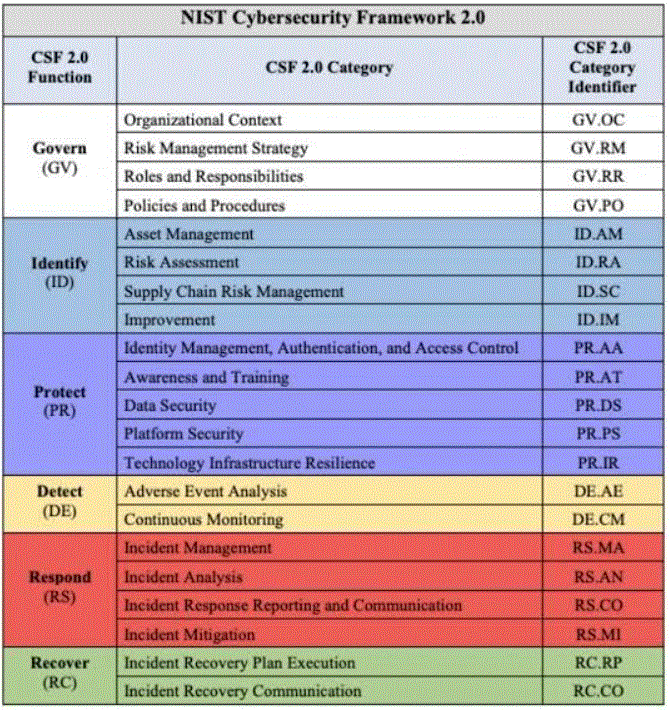
The National Institute of Standards and Technology (NIST) officially released version 2.0 of their Cybersecurity Framework in February 2024. This update is not merely an incremental change but a comprehensive overhaul that addresses the changing cyber threat landscape and incorporates feedback from a wide range of stakeholders.
Here are 15 key differences between NIST CSF 1.1 and 2.0:
1. Introduction of the “Govern” Function: The most significant change in NIST CSF 2.0 is the introduction of a new function, “Govern”. This function recognizes that Cyber Governance is extremely important.
2. Addition of ID.RA-10: This new subcategory emphasizes the importance of assessing critical suppliers prior to acquisition.
3. Removal of PR.DS-09: This subcategory, which focused on managing data throughout its life cycle, including destruction, has been removed and moved to ID.AM-08.
4. Supply Chain Security: 2.0 places a stronger emphasis on supply chain security.
5. AI Risk Management: 2.0 includes guidelines on artificial intelligence risk management.
6. Zero-Trust Architecture: The new version provides guidance on zero-trust architecture.
7. Edited Definitions: The definitions have been edited, mostly softening obligations placed on organizations.
8. Emphasis on Comprehension: CSF 2.0 places an added emphasis on comprehension.
9. Stakeholder Obligations: CSF 2.0 places more emphasis on stakeholder obligations.
10. Integration of Privacy Considerations: Privacy considerations are integrated throughout the framework to address the growing importance of privacy in cybersecurity.
11. Number of Categories and Subcategories: NIST CSF 1.1 bolstered 22 categories and 108 subcategories. NIST CSF 2.0 contains 23 categories and 106 subcategories.
12. Streamlined Usability: CSF 2.0 introduces several major updates designed to streamline the framework’s usability and aligns more closely with ISO 27001 standards.
13. Enhanced Effectiveness: CSF 2.0 enhances its effectiveness in addressing contemporary cybersecurity challenges.
14. Reflection of Advances in Technology: The move to CSF 2.0 reflects advances in technology.
15. Shifts in Cyber Threats: CSF 2.0 reflects shifts in cyber threats.
Stay safe and secure!
Please note that this is a simplified summary and for a more detailed comparison, you may want to refer to the official NIST documents or other detailed resources in their site.
I hope you find this post useful and informative. Please feel free to share your thoughts and feedback in the comments. Stay tuned for more posts on cybersecurity, risk and compliance in the coming days.