Risk Treatment is the process of selecting and applying appropriate measures to reduce the impact and likelihood of cyber threats to information systems.
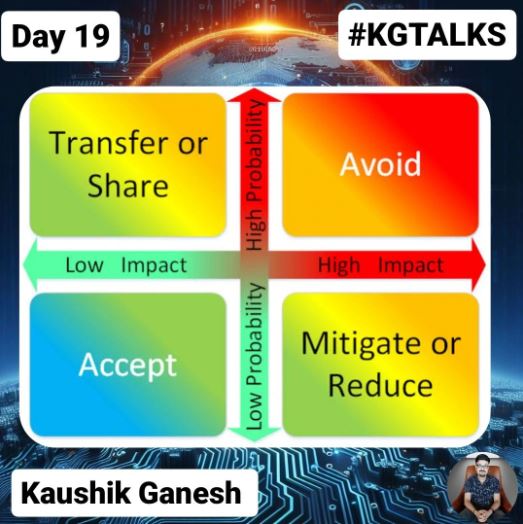
There are four main types of risk treatment options:
1. Avoidance: This means avoiding the activity or process that creates the risk altogether. For example, if using a public Wi-Fi network is too risky, you can avoid connecting to it and use a secure VPN instead.
2. Transfer: This means shifting the risk to another party, such as an insurance company or a third-party service provider. For example, if storing sensitive data on your own servers is too risky, you can transfer the risk to a insurance company that offers data breach coverage.
3. Reduction: This means implementing controls or safeguards to lower the level of risk to an acceptable level. For example, if phishing emails are a common risk, you can reduce the risk by training your staff on how to identify and report them, and by installing anti-malware software on your devices.
4. Acceptance: This means acknowledge the risk and its potential consequences, and deciding not to take any action to mitigate it. This option is usually chosen when the risk is low or the cost of treatment is too high. For example, if the risk of a power outage is low and the impact is minimal, you can accept the risk and not invest in a backup generator.
Here is an example of how a company can apply these risk treatment options to a specific cyber threat such as a ransomware attack, which is a type of malware that encrypts the victim’s data and demands a ransom for the decryption key.
1. Avoidance: They can avoid the risk of a ransomware attack by not using any software or hardware that is vulnerable to this type of malware, such as outdated operating systems or unpatched applications.
2. Transfer: They can transfer the risk of a ransomware attack by purchasing a cyber insurance policy that covers the cost of ransom payments and data recovery in case of an attack.
3. Reduction: They can reduce the risk of a ransomware attack by implementing security best practices, such as regularly updating and backing up their data, using strong passwords and multi-factor authentication, and educating their employees on how to spot and avoid suspicious links and attachments.
4. Acceptance: They can accept the risk of a ransomware attack by deciding that the likelihood and impact of an attack are low enough to justify the risk, and that they have sufficient resources and capabilities to deal with the consequences if an attack occurs.
I hope you find this post useful and informative. Please feel free to share your thoughts and feedback in the comments. Stay tuned for more posts on cybersecurity, risk and compliance in the coming days.