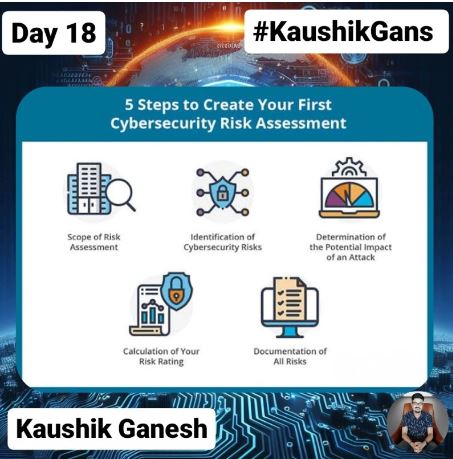
A risk assessment is a process of identifying, analyzing, and evaluating the potential cyber threats and vulnerabilities that could affect an organization’s information and information systems. The purpose of a risk assessment is to help the organization prioritize the risks and take appropriate actions to reduce or eliminate them. A risk assessment typically involves the following steps:
1. Identify and document the network assets and their vulnerabilities.
This means listing all the devices, software, data, and users that are part of the organization’s IT infrastructure and finding out their weaknesses or flaws that could be exploited by cyber attackers.
2. Identify and use sources of cyber threat intelligence.
This means gathering information from internal and external sources about the current and emerging cyber threats that could target the organization or its industry sector. For example, this could include reports from security agencies, vendors, or experts, as well as historical data from previous cyber incidents.
3. Identify and document internal and external threats. This means scanning the network for signs of compromise, such as malware, unauthorized access, or configuration changes, as well as assessing the likelihood and impact of different types of cyber attacks, such as ransomware, phishing, or denial-of-service.
4. Identify potential mission impacts.
This means estimating the consequences of a cyber attack on the organization’s business operations, reputation, and finances, as well as the legal and regulatory implications. For example, this could include loss of productivity, customer trust, revenue, or data, as well as fines, lawsuits, or compliance violations.
5. Use threats, vulnerabilities, likelihoods, and impacts to determine risk.
This means quantifying the level of risk for each asset and threat combination, using a scale such as low, medium, or high, or a numerical value. This helps to compare and prioritize the risks and decide which ones need immediate attention or mitigation.
A risk assessment is an essential part of cybersecurity risk management, as it provides a clear picture of the organization’s cyber posture and helps to allocate resources and implement controls to protect the organization from cyber threats. A risk assessment should be performed regularly and updated whenever there are changes in the network, the threat landscape, or the business objectives.
I hope you find this post useful and informative. Please feel free to share your thoughts and feedback in the comments. Stay tuned for more posts on cybersecurity, risk and compliance in the coming days