What is the CIA Triad?
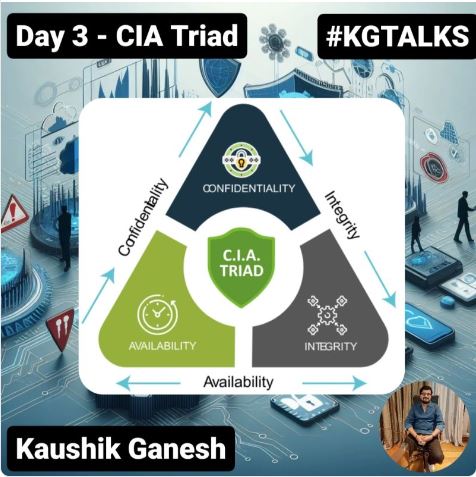
The CIA Triad is a well established framework for information security, based on three core values: Confidentiality, Integrity, and Availability. These values guide the design and implementation of security policies within an organization, ensuring that data is protected, reliable, and accessible.
Confidentiality – This means keeping information private and only allowing authorized parties to access it. It’s like having a secret language that only you and your trusted friends can understand. Methods such as encryption, multi-factor authentication, and biometrics can help achieve this goal.
Integrity – This means keeping information accurate and preventing unauthorized changes. It’s like making sure that the message you send is the same as the message that is received. Tools such as checksums, hashes, and digital signatures can help verify this property.
Availability – This means keeping information available and ready for use by authorized users. It’s like making sure that your devices are working properly, that you have a backup plan in case of failure, and that you have a good internet connection. Techniques such as maintenance, redundancy, and load balancing can help ensure this quality.
The CIA Triad is not just a theoretical concept; it’s a practical standard for measuring the effectiveness of your cybersecurity strategy. The three values are interdependent and complementary, forming a strong defence against cyber threats. Your data’s Confidentiality, Integrity, and Availability are essential. They are the pillars of a solid cybersecurity architecture. So, how much your cybersecurity strategy align with the CIA Triad plays a major role!
I hope you find this post useful and informative. Please feel free to share your feedback in the comments. Stay tuned for more posts on cybersecurity, risk and compliance in the coming days.